00Cybersecurity / Clear by design

See the risk.
Strengthen the system.

Security assessments, practical hardening and ongoing monitoring for businesses that need a clearer view of their IT environment.

Explore services
Optical inspection lens over white and silver circuitry
OPTICAL CLARITY / SYSTEM DETAIL01—07
01Diagnosis / Establish the facts

Start with a clearer
picture of your exposure.

Understand where risk sits before deciding what to change. Two focused assessments, each with a different purpose.

SERVICE 01 / RISK

Cybersecurity Risk Assessment

A review of your IT environment, existing controls and access practices. We connect technical observations to the business processes that depend on them.

  • IT environment and control review
  • Access practices and risk prioritization
  • Practical recommendations for next steps
$1,500
SERVICE 02 / VULNERABILITY

Vulnerability Assessment

Identify and assess weaknesses across agreed systems, devices, networks and applications. Findings are reviewed in context so the next steps are easier to prioritize.

  • Agreed asset and application scope
  • Vulnerability identification and analysis
  • Documented findings and remediation priorities
$1,250
Close inspection of a semiconductor wafer under white light

USD. Asset counts, access requirements and deliverables are confirmed in a written scope before work begins.

02Hardening / Reduce unnecessary exposure

Stronger settings.
Fewer open doors.

Targeted work on your network, cloud accounts and business workspace, with changes agreed before implementation.

03 / NETWORK

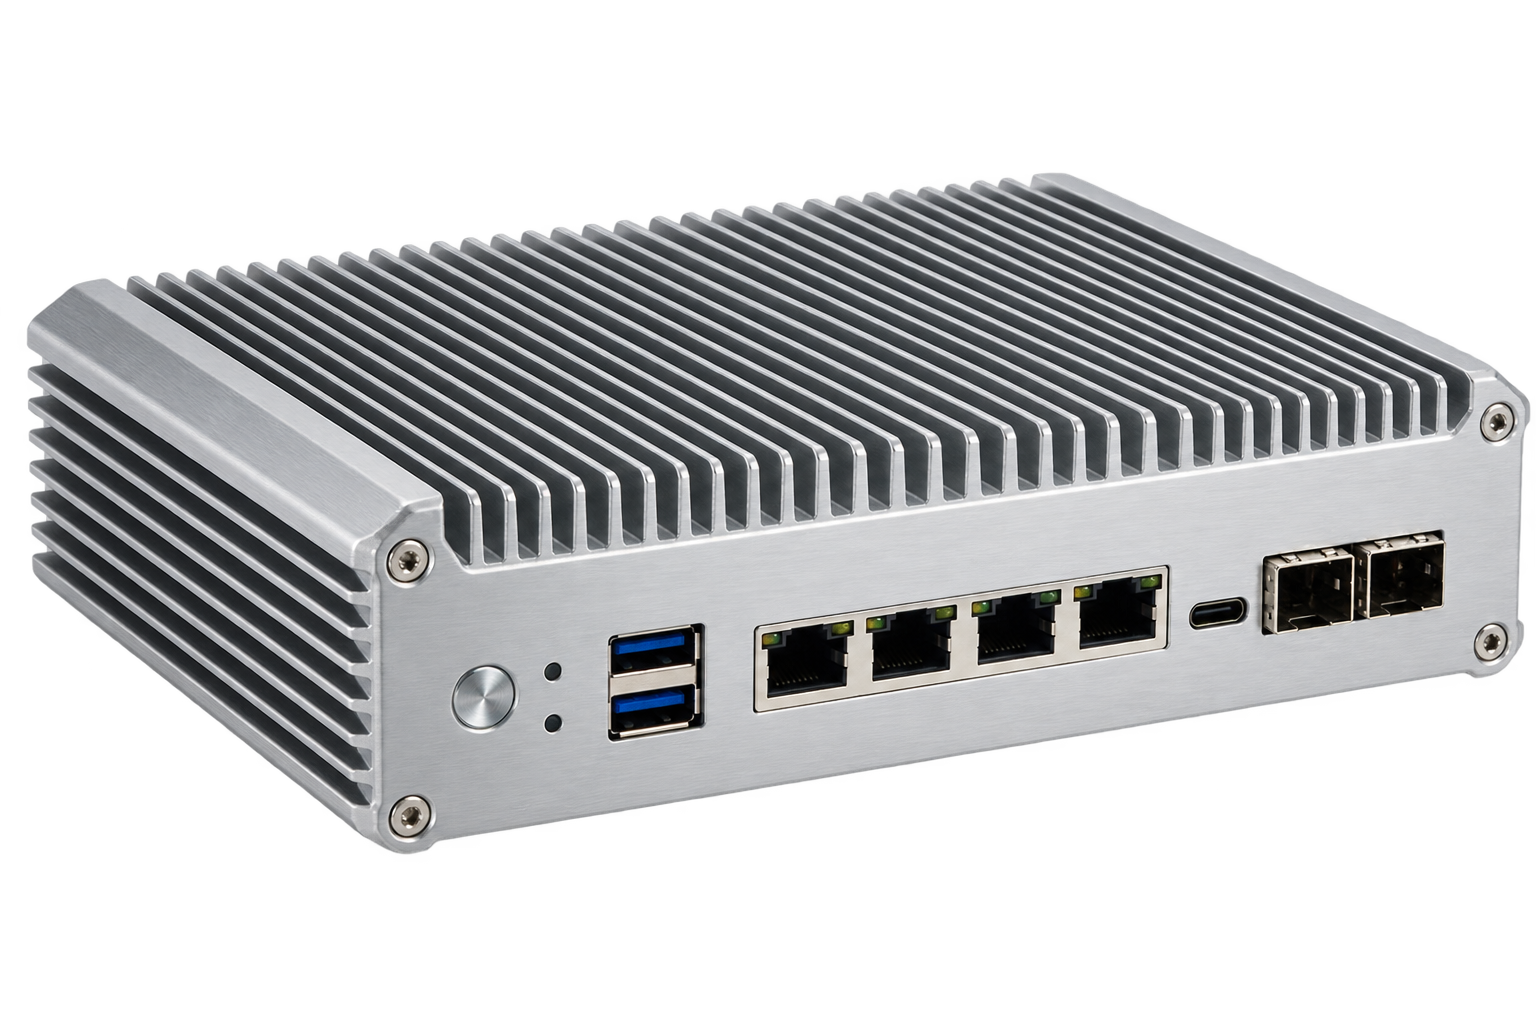
Network Security Audit & Hardening

Make network access deliberate. Review firewall rules, network configurations, access controls and security policies, then implement the improvements agreed for your environment.

Configuration review / Access controls / Approved changes
$1,800
Photographic aluminum network module
04 / CLOUD

Cloud Security Review

Bring cloud permissions into focus. Examine user permissions, account settings and data access in the agreed cloud environment. Identify common misconfigurations and document practical changes.

Permission review / Account settings / Data exposure
$1,650
Photographic enterprise storage module
05 / WORKSPACE

Microsoft 365 / Google Workspace Security Hardening

Tighten the tools your team uses daily. Review administrator access, authentication, account permissions and sharing policies in Microsoft 365 or Google Workspace. Improve configurations within the approved scope.

Authentication / Admin access / Sharing policies
$950
Photographic biometric security key

USD. A Cloud Security Review assesses the environment; implementation beyond the agreed review is scoped separately.

03Penetration testing / Test the assumptions

Find the weakness
under pressure.

$4,500 USD

Controlled testing of selected systems, applications or network infrastructure to identify exploitable vulnerabilities. The objective is a useful account of what can be exploited, why it matters and how to address it.

Written authorization, target boundaries, testing windows and escalation contacts are required before testing begins.

A steel testing ram compressing a white polymer specimen
DEFINED TARGETSCONTROLLED TESTINGDOCUMENTED FINDINGSREMEDIATION GUIDANCE
Engineer reviewing a computer and taking notes in a bright office
04Response / Maintain a watchful view

When the situation
needs attention.

Incident Response & Recovery Support

Technical assistance to investigate an incident, contain affected systems, identify contributing causes and support recovery decisions.

$250/hour

Managed Security Monitoring

Ongoing review of security events, vulnerabilities and suspicious activity, with endpoint protection oversight and recurring security recommendations.

$1,500/month

USD. Coverage, monitoring hours and response arrangements are defined in the service agreement. A website enquiry does not activate incident support.

05Method / From observation to action

A defined scope.
A useful outcome.

Good security work starts with clear boundaries and ends with decisions your team can act on.

01

Define the boundary.

We identify the systems, accounts and business priorities involved. Access arrangements, responsibilities and testing permissions are agreed before technical work starts.

02

Examine the environment.

The review follows the agreed scope. Findings are documented with enough context to distinguish an immediate concern from an improvement that can be planned.

03

Make the next step clear.

Recommendations connect each issue to an action. Implementation is approved in advance, and any work outside the original scope is discussed before proceeding.

04

Review what changed.

Where included in the engagement, the agreed changes are checked and remaining items are recorded. Ongoing monitoring is available as a separately defined service.

06Working together / Business context matters

Security work that
fits the environment.

Managers Anonimos works with businesses that need to understand risk, improve everyday security settings or establish a more consistent view of activity across their systems.

Questions about scope and access ↗
01

For owners and operators

A clear account of technical risks and proposed actions, without requiring every decision-maker to be a security specialist.

02

Alongside internal IT

A defined engagement that can complement your existing IT team, with responsibilities and change approvals agreed from the start.

03

For cloud-based teams

Attention to permissions, authentication and sharing in the accounts and workspaces used to run day-to-day business.

07Client feedback / Service reviews

What clients say.

Feedback on assessments, hardening, testing and ongoing security support.

01 / 08
★★★★★Alexander V.Cybersecurity Risk Assessment
“We had not reviewed our IT infrastructure in a long time, so we decided to commission a comprehensive risk assessment. The Managers Anonimos team took a thorough look at our systems, policies and access management practices. The report was detailed and practical: no unnecessary filler, just real threats and clear steps to address them. A very professional approach. We now understand what to prioritize next.”
★★★★★Elena S.Vulnerability Assessment
“Thank you to the Managers Anonimos specialists for a thorough vulnerability assessment. They found several critical weaknesses in our business applications and devices that we had not known about. Their detailed analysis helped us close those gaps before anyone could exploit them. I would definitely recommend them.”
★★★★★Mikhail T.Network Security Audit & Hardening
“We commissioned a network security audit and hardening project. The specialists checked our router configurations, reconfigured our firewalls and updated our security policies. Since implementing their recommendations, the network has been running reliably, and we feel completely confident that our data is protected against external threats. An excellent investment in business security.”
★★★★★Dmitry K.Cloud Security Review
“We moved fully to the cloud last year, but we still had doubts about whether everything was configured correctly. We booked a Cloud Security Review. The Managers Anonimos team identified excessive access permissions for some users and helped us configure data protection properly in our cloud environment. We now feel much more comfortable with our infrastructure.”
★★★★★Anna L.Microsoft 365 / Google Workspace Security Hardening
“We are a small team, but we rely heavily on cloud workspaces. We chose the service to improve the security of our business email and shared drives. The work was completed quickly, with little disruption to our staff. They strengthened authentication, removed unnecessary administrator privileges and secured file sharing. At this price, it is a must-have for a modern business.”
★★★★★Viktor R.Penetration Testing
“The penetration test carried out by Managers Anonimos exceeded our expectations. It was a realistic, carefully planned attack against our system. The specialists clearly demonstrated how an attacker could gain access to our databases and gave us comprehensive instructions on how to protect them. The level of technical expertise was outstanding.”
★★★★★Sergey M.Incident Response & Recovery Support
“We contacted Managers Anonimos in an emergency after detecting suspicious activity on our internal network. The team responded immediately. They helped contain the incident, isolated the compromised systems and quickly identified the source of the problem. Without their prompt assistance, the financial and reputational damage could have been catastrophic. Thank you for helping us through it.”
★★★★★Olga N.Managed Security Monitoring
“After a one-time audit, we decided to move to an ongoing service. The Managers Anonimos specialists now monitor our endpoints, network and suspicious activity around the clock. Each month, we receive clear reports and fresh recommendations for improving our systems. For us, this has been more cost-effective and reliable than hiring an in-house security team.”
08Questions / Set clear expectations

Before
we begin.

Scope, permissions, pricing and the practical details of an engagement.

Which assessment should we start with?

A Cybersecurity Risk Assessment examines the environment and its controls in business context. A Vulnerability Assessment focuses on identifying and analyzing technical weaknesses in the agreed systems. The right starting point depends on the decisions you need to make.

What do the displayed prices cover?

Prices are in US dollars and relate to the named service. Asset counts, environments, access requirements and deliverables are confirmed before work begins. Incident support is billed hourly and monitoring is a monthly service. Additional scope and any applicable taxes are stated in the written agreement.

Will you make changes without approval?

Implementation work requires an agreed scope and approval. Review services identify issues and recommendations; they do not automatically include every remediation action. Testing boundaries, access arrangements and change responsibilities are confirmed in advance.

Can you test systems owned by another provider?

Only when appropriate authorization is in place. You must have the right to permit testing of each target, including any required third-party approval. Targets and testing windows must be recorded before penetration testing starts.

Is incident support immediately available?

Availability, start time and response arrangements must be confirmed directly. Submitting a website enquiry does not create an emergency response commitment or activate monitoring. If an incident is active, contact the business directly using the details in the project section.

Do you guarantee that a business cannot be breached?

No. Assessments and controls can reduce risk, but no engagement can identify every weakness or prevent every incident. Findings reflect the agreed scope, the information available and the environment at the time of the work.

What should we include in an enquiry?

Describe the service you need, the general type of environment and the business concern. Do not include passwords, access tokens, confidential reports or sensitive customer data. Detailed technical information can be exchanged through an agreed channel after the scope is discussed.

How does the website form work?

The current form validates the fields and displays a confirmation in your browser. It does not send an email, open a service ticket or start an engagement. To contact Managers Anonimos, use the email address or phone number displayed in the project section.

09Project enquiry / Establish a starting point

Put your next
security decision
in focus.

Tell us what needs attention and which environment is involved. Begin with a service enquiry or a general discussion of your security priorities.

Email

security@managersanonimos.com

Address

30 N Gould St Ste N,
Sheridan, WY 82801

Phone

+1 307 677 9549

The form is a browser-only demonstration. For an actual enquiry, contact Managers Anonimos directly using the details above. Do not include credentials or sensitive system information.

Discuss your security needs

Select a service and describe the business concern. All fields are required.

Your entries stay in this page. No email or service ticket is created.